Personal Data in Modern Tech: Understanding Your Digital Privacy Rights in the Age of AI and Cloud Platforms
Personal Data in Modern Tech
Understanding Your Digital Privacy Rights in the Age of AI, Mobile Money, and Cloud Platforms
Every time you unlock your smartphone with your fingerprint, complete a mobile money transfer, browse an e-commerce catalog, or query an AI assistant, you leave behind an intricate digital footprint. In today's hyper-connected landscape, personal data is the bedrock of the global digital economy. Yet millions of citizens, consumers, and enterprise executives across Africa and the world navigate daily online interactions without a clear understanding of what data is harvested, where it is stored, how algorithms weaponize it, and what statutory rights exist to protect them.
At Initiative Tech Solutions (ITS) Ltd, we believe that data privacy is not an optional luxury or a legal footnote—it is the foundational prerequisite of democratic commerce, consumer sovereignty, and enterprise trust. As East Africa cements its position as a global leader in digital transformation and fintech innovation, understanding the legal and technical boundaries of personal data protection is indispensable.
"True cybersecurity begins with respect for human agency. When engineering enterprise software, privacy cannot be an afterthought bolted on after deployment. It must be architected from the database layer upward using zero-knowledge principles, strict data minimization, and sovereign on-device execution."
Chief Engineer, ITS Ltd
1. What Actually Constitutes "Personal Data" in 2026?
Historically, legal statutes defined personal data narrowly as your legal name, national identity number, and physical residence. Today, in an era of ubiquitous sensor arrays, persistent browser cookies, telemetry APIs, and deep learning algorithms, personal data encompasses any information relating to an identified or identifiable natural person.
01. Direct Identifiers & Biometrics
Names, telephone numbers, physical and email addresses, national ID cards, passport credentials, high-resolution facial geometry, fingerprint templates, and voiceprints used during KYC (Know Your Customer) verifications. Biometrics represent irreplaceable data—if compromised, a user cannot simply reset their face or fingerprints like a password.
02. Behavioral & Telemetry Footprints
GPS coordinate histories, cell tower handoff timestamps, browser canvas fingerprinting, device hardware UUIDs, IP addresses, application dwell times, scroll depths, and Wi-Fi BSSID triangulation records that map daily movement patterns with pinpoint accuracy.
03. Financial Graphs & Transaction Trails
Mobile money transaction histories (MTN MoMo, Airtel Money, M-Pesa), micro-lending repayment records, bank account numbers, merchant POS till payments, utility purchase habits, and algorithmic credit risk scores generated by fintech aggregators.
04. Generative AI Prompts & Interaction Data
Natural language prompts, uploaded corporate balance sheets, legal contract excerpts, code snippets, and conversational transcripts submitted to third-party cloud LLMs. These inputs are frequently ingested into central training corpora without user consent.
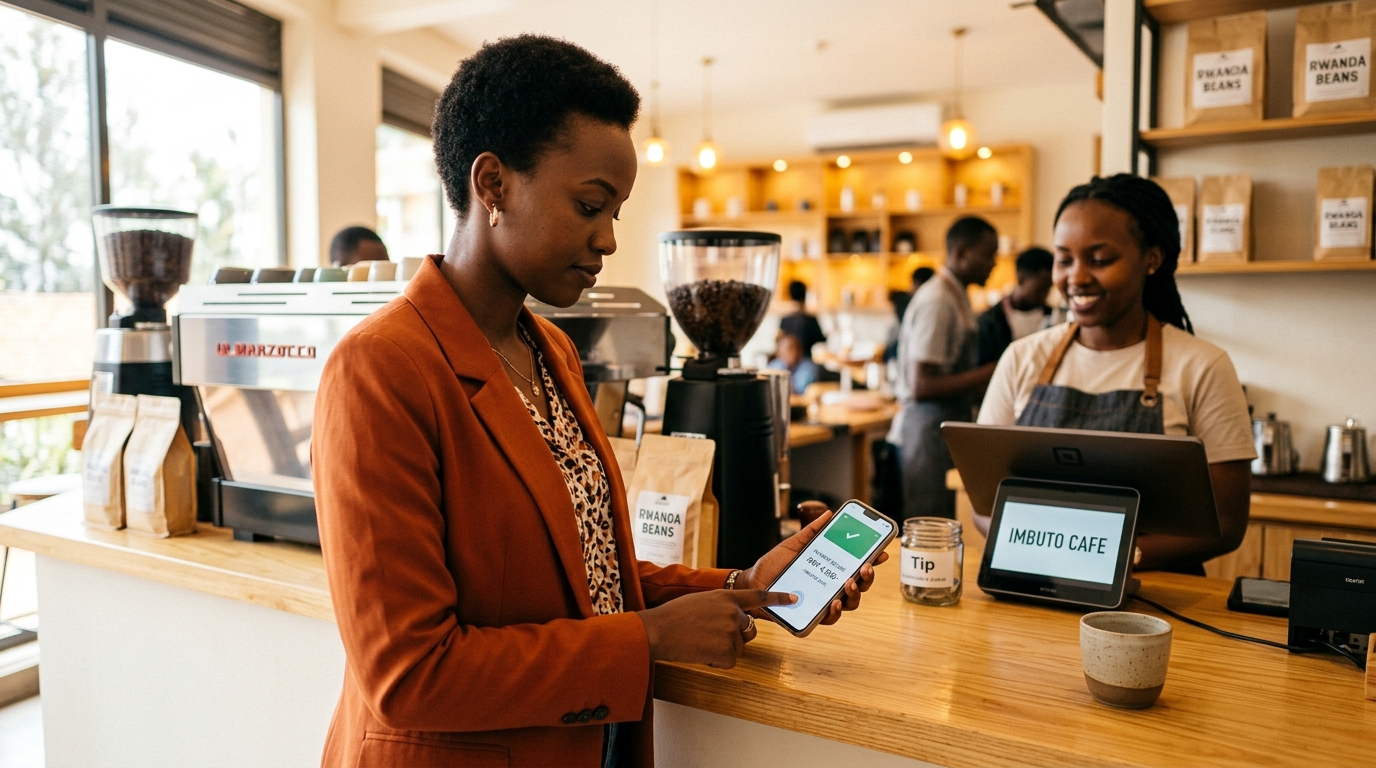
Figure 1: Every digital transaction—from mobile money checkouts to biometric unlocks—generates sensitive metadata that requires legal protection and cryptographic security.
2. The 5 Universal Privacy Rights Every Digital Citizen Holds
Modern privacy jurisprudence—anchored in Rwanda's statutory framework and international instruments like the European Union's General Data Protection Regulation (GDPR) and the African Union's Malabo Convention—grants individuals five non-negotiable rights over their personal information:
The Right to be Informed (Transparency & Plain Language)
You have the right to know exactly who is collecting your data, the legitimate legal basis for processing it, the precise operational purpose it serves, how long it will be retained, and which third parties will access it.
Real-World Scenario: A mobile banking app cannot bury a clause on page 40 of a terms-of-service agreement stating that your transaction history will be sold to advertising brokers. Consent must be freely given, specific, informed, and unambiguous.
The Right of Access & Data Portability
You can formally submit a Data Subject Access Request (DSAR) to any company holding your data. The organization is legally mandated to provide a complete copy of all your records free of charge, delivered in a structured, commonly used, and machine-readable format (e.g., JSON, CSV).
Real-World Scenario: If you transition your enterprise operations or personal accounts from one SaaS or telecom vendor to another, the provider must export your complete historical data without artificial vendor lock-in hurdles.
The Right to Rectification (Correction of Inaccuracies)
If a financial institution, government registry, healthcare provider, or software platform maintains incorrect, outdated, or incomplete data about you, you have the statutory right to compel immediate correction without undue delay.
Real-World Scenario: If an erroneous default record in a credit bureau ledger falsely lowers your financial scoring, the institution must rectify the record across all downstream partner databases upon verification.
The Right to Erasure ("The Right to be Forgotten")
When you terminate a digital account, withdraw previously granted consent, or when your data is no longer necessary for the original legitimate purpose for which it was gathered, you have the legal right to demand the total, permanent purge of your records from production databases and cold backups.
Real-World Scenario: When an employee departs a company or a user cancels an e-commerce subscription, the vendor cannot silently retain payment cards or behavioral profiles for marketing campaigns.
The Right to Object to Automated Profiling & Algorithmic Decisions
You retain the right not to be subject to decisions based solely on automated processing—including AI-driven profiling—that produce legal or similarly significant effects concerning your livelihood, credit terms, employment candidacy, or insurance premiums.
Real-World Scenario: If an automated recruitment algorithm filters out your job application, you have the right to request human intervention, contest the algorithmic assessment, and understand the logic behind the decision.
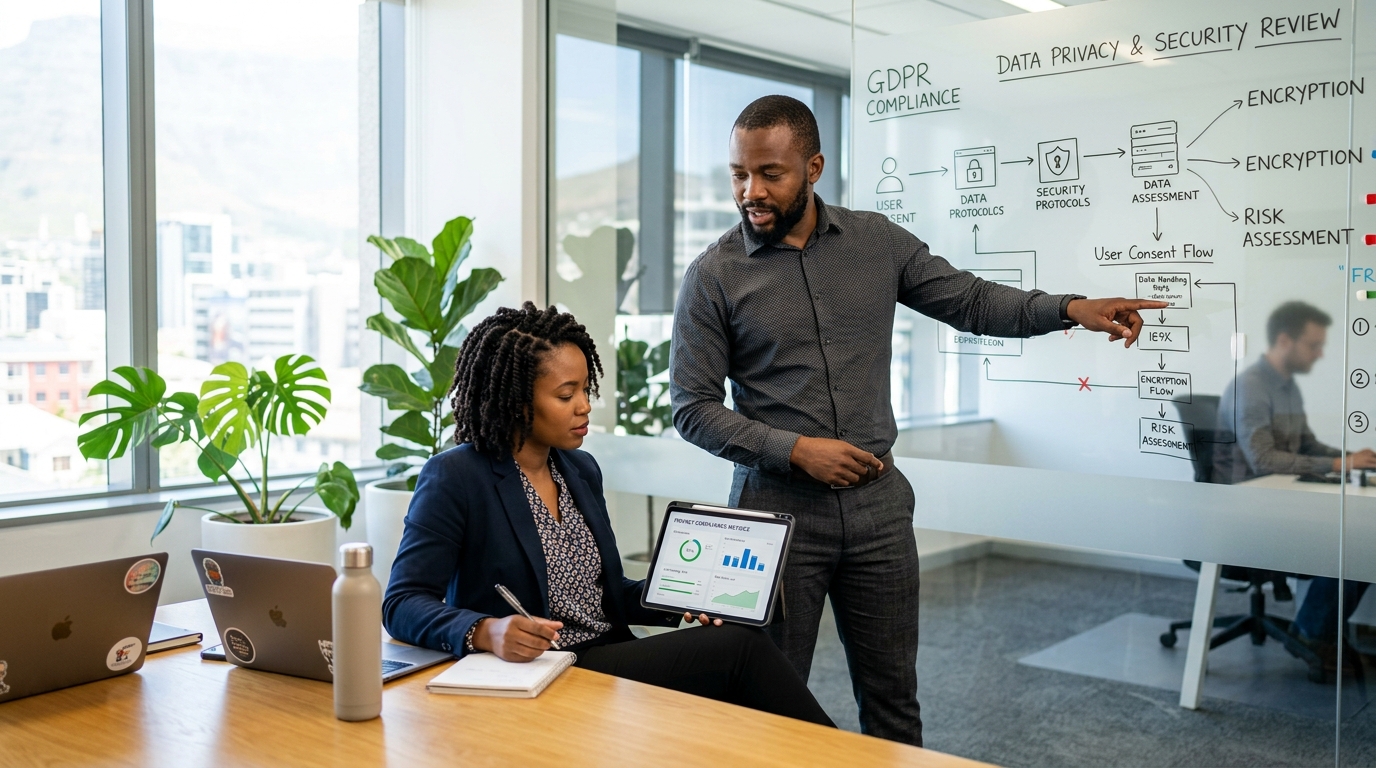
Figure 2: Corporate governance and security teams conducting a comprehensive Data Protection Impact Assessment (DPIA) and mapping consent workflows.
3. Rwanda’s Legal Shield: Law Nº 058/2021 & NCSA Directives
Rwanda has established one of Africa's most sophisticated and rigorously enforced legal protections through Law Nº 058/2021 of 13/10/2021 relating to the protection of personal data and privacy. Overseen by the National Cyber Security Authority (NCSA) and its dedicated Data Protection Office (DPO), this law creates a structured regulatory environment with strict obligations for commercial and public organizations:
| Core Legal Requirement | Statutory Obligation (Law Nº 058/2021) | Impact on Consumers & Enterprises |
|---|---|---|
| Mandatory Registration | Data Controllers and Processors must register with NCSA / DPO before processing personal data. | Guarantees that companies handling your data are officially accountable and audited. |
| Data Minimization | Collection is restricted exclusively to what is strictly necessary for specified, explicit, and legitimate purposes. | Prevents apps from harvesting contact lists, camera feeds, or location data unnecessarily. |
| Cross-Border Transfers | Data storage outside Rwanda requires explicit authorization or verified equivalent legal protections. | Protects national data sovereignty and shields Rwandan citizens from foreign surveillance laws. |
| Breach Notification | Controllers must notify the NCSA within 48 hours of discovering a personal data breach. | Ensures rapid incident containment and transparent consumer alerting without corporate cover-ups. |
| Data Protection Officer | Designation of a certified DPO is mandatory for organizations handling sensitive or large-scale data. | Provides consumers with a designated executive point of contact to enforce privacy rights. |
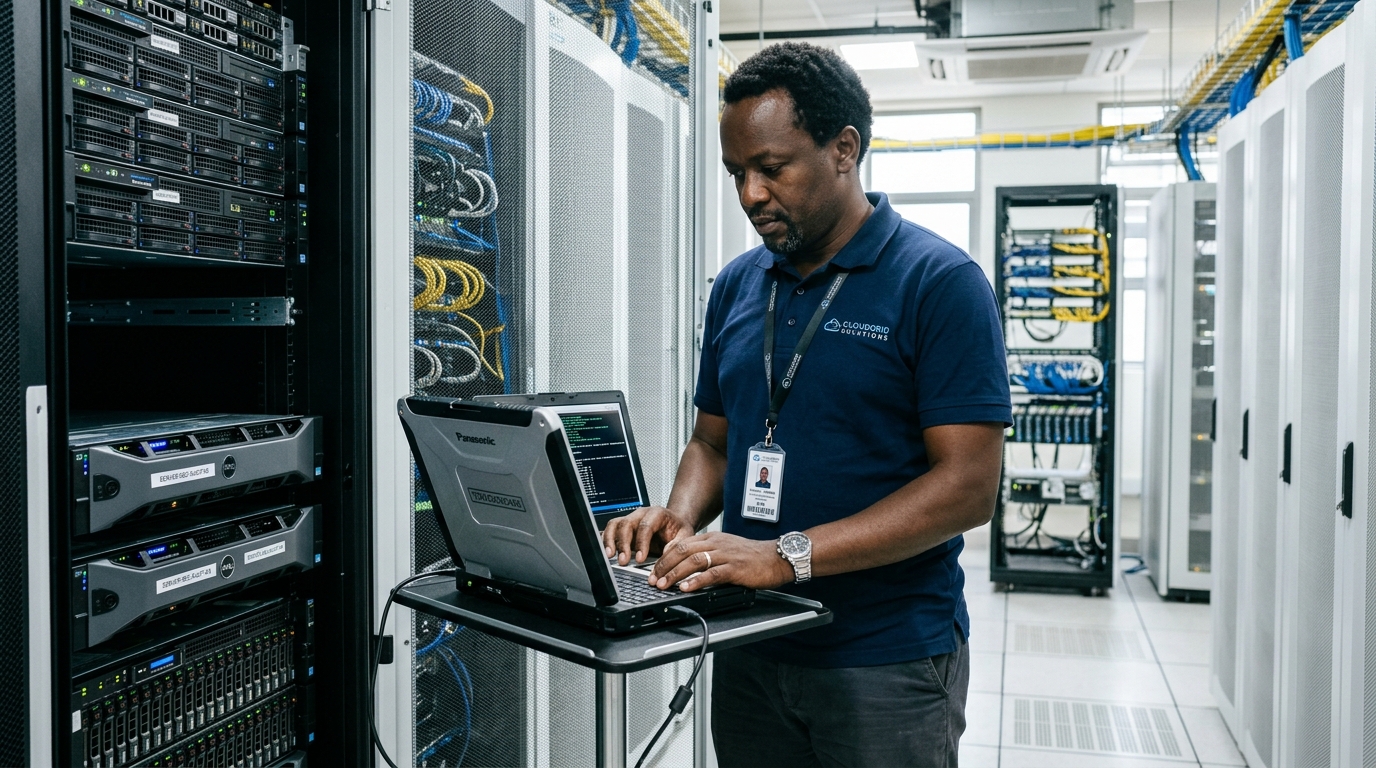
Figure 3: On-premise sovereign data center infrastructure ensuring strict compliance with national cross-border data transfer regulations.
4. The AI Dilemma: Cloud LLMs vs. Sovereign On-Device Intelligence
The explosive rise of cloud-hosted artificial intelligence platforms has opened an alarming new vector for data privacy violations. When business employees, legal practitioners, healthcare workers, or students paste text into generic public AI chat tools, that data traverses public internet routers into overseas data centers. In many standard consumer terms of service, user prompt histories and attached spreadsheets are indexed, retained, and utilized to fine-tune subsequent iterations of commercial models.
This creates a severe "Shadow AI" vulnerability where proprietary financial strategies, patient health records, trade secrets, and personally identifiable client rosters inadvertently leak into third-party cloud datasets.
The ITS Ltd Sovereign Architecture Solution
To permanently eliminate third-party AI data leaks, Initiative Tech Solutions (ITS) Ltd engineers Sovereign On-Device AI Models across the Inzora Business Suite (IBS) and Inzora Security.
Zero Data Egress
Inference executes locally on workstations and branch servers using quantized GGUF/AWQ models. No prompt payload ever leaves the local network.
Full Offline Resilience
Enterprise AI assistants, automated stock forecasting, and anomaly detection operate uninterrupted during fiber and internet service outages.
Total IP Protection
Financial records, employee payrolls, and customer transactions remain cryptographically locked behind client-controlled encryption keys.
5. Practical Digital Privacy Hygiene: The Essential Playbook
Whether you are an individual citizen safeguarding your private life or a business executive protecting corporate assets, disciplined digital hygiene minimizes your vulnerability to automated data mining and criminal cyber attacks:
Review app settings on iOS and Android monthly. Revoke background location, microphone, camera, and contact access for apps that do not require them to perform their primary function.
Move away from SMS-based verification codes, which are vulnerable to SIM-swap fraud. Adopt FIDO2 hardware security keys (e.g., YubiKeys) or dedicated authenticator applications (TOTP).
Never perform mobile banking, access enterprise portals, or enter payment credentials on open public Wi-Fi without an authenticated, encrypted VPN tunnel using WireGuard or IPsec.
For sensitive personal and business discussions, prioritize platforms implementing the open-source Signal Protocol where encryption keys exist solely on the communicating endpoints.
Before adopting any third-party SaaS or AI tool for business operations, verify whether the vendor offers zero-data-retention agreements and explicitly excludes your data from model training.
When discontinuing an online service or mobile app, do not simply delete the app icon. Formally submit an in-app data deletion request and demand written confirmation of account eradication.
Achieve Total Data Privacy Compliance with ITS Ltd
Is your business fully compliant with Rwanda’s Data Protection Law (Law Nº 058/2021) and international privacy frameworks? Partner with Initiative Tech Solutions (ITS) Ltd at Norrsken House Kigali for comprehensive Data Protection Impact Assessments (DPIA), penetration testing, zero-trust system architecture, and custom enterprise software development.
Article Intelligence
Strategic Alliance
Enterprise digital alignment requires tactical precision. Partner with the ITS Ltd implementation team.
Further Intelligence
Browse All Articles →
Privilege Auditing: The Critical Cornerstone of Business Cybersecurity
In a recent expert feature on SafetyDetectives, Irumva Yves Ngabonziza, Chief Engineer at ITS Ltd, shared why auditing user privileges and implementing the Principle of Least Privilege is essential to prevent costly data breaches.
The Power of Inzora Security Software: Comprehensive Cybersecurity Solutions
Discover how Inzora Security Software provides comprehensive cybersecurity solutions to protect your business from evolving digital threats with advanced threat detection and data protection.